Cyber Security7 Mar 2024 · 3 min read
Why 24/7 SOC monitoring matters for growing teams
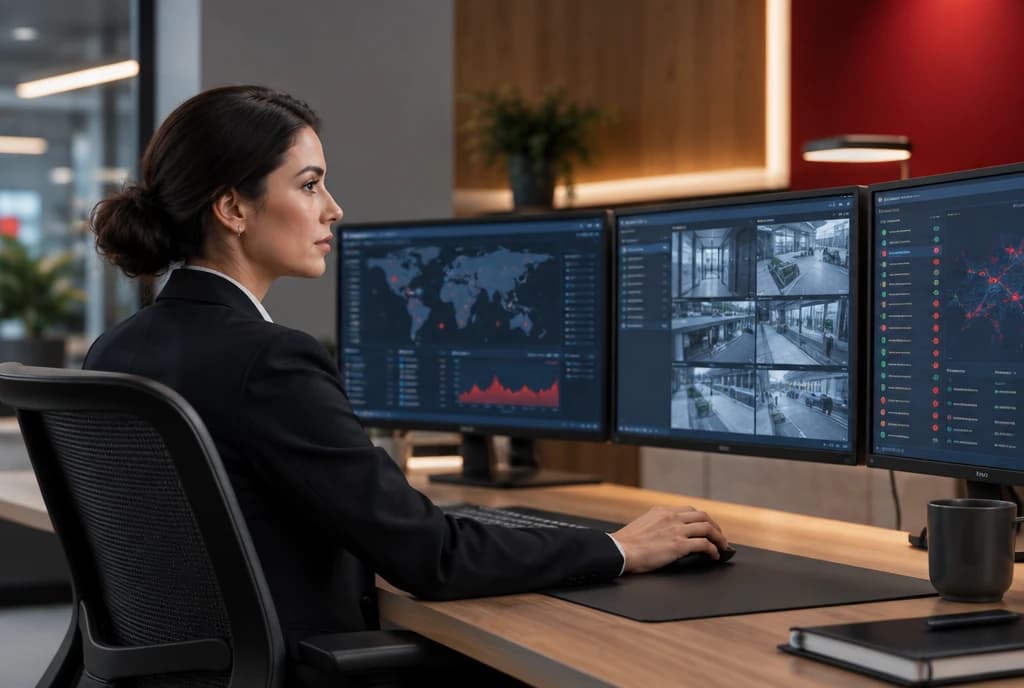
Threats do not keep office hours. Round-the-clock monitoring turns alerts into action before they turn into incidents.
Firewalls, endpoint protection and email filters do an important job, but they also produce a constant stream of alerts. Most are harmless. A few are the early signs of a real attack. Without someone watching, the important ones are easy to miss, especially outside office hours.
A security operations centre, or SOC, is the team and tooling that watches those signals around the clock, investigates what looks wrong and responds before a small issue becomes an incident.
Attacks don't keep office hours
Attackers know that many businesses are only watched during the working day. Suspicious logins, mass file changes and unusual data transfers often happen late at night, at weekends or during holidays, when response is slowest.
Round-the-clock monitoring means someone is always looking, and the time between something going wrong and someone acting on it shrinks from days to minutes.
What a SOC actually does
- Collects logs and alerts from firewalls, servers, laptops, email and cloud services in one place.
- Correlates events, so a strange login followed by a large download is seen as one story rather than two unrelated alerts.
- Investigates anomalies and separates genuine threats from false alarms.
- Responds: isolating a device, disabling an account or blocking an address, following an agreed playbook.
- Reports regularly, so leadership can see risks, trends and what was handled.
Why it suits growing teams
Building an in-house security team that covers every hour of every day is expensive and hard to staff. For most growing businesses, a managed SOC gives access to experienced analysts and mature tools at a fraction of that cost, and it scales as you add people, sites and cloud services.
It also frees your internal IT staff to focus on projects and support, instead of trying to watch dashboards in their spare time.
Getting the foundations right
Monitoring works best on top of solid basics. Before or alongside a SOC, make sure the essentials are in place.
- Multi-factor authentication on email, VPN and admin accounts.
- Next-generation firewalls and endpoint protection on every device.
- Email security that filters phishing and malicious attachments.
- Regular patching of operating systems, applications and network devices.
- Clear ownership: who the SOC contacts, and who can approve urgent actions.
Visibility for leadership and compliance
Regular SOC reports give management a clear view of security posture: what was detected, what was blocked and what needs attention. That evidence is increasingly important for audits, customer questionnaires and cyber insurance.
How we help
Our 24/7 SOC monitoring connects to your firewalls, endpoints, email and cloud services, with analysts who investigate and respond at any hour. Combined with the right security stack, it gives growing teams enterprise-level protection without building a security department from scratch.